AI API Penetration Testing
Autonomous AI agents find every API you expose, including the undocumented ones, exploit them with proof, and chain API flaws into full attack paths across apps and infrastructure. Continuously, not once a year.
What is AI API penetration testing?
AI API penetration testing uses autonomous AI agents to discover, safely exploit, and validate security flaws in REST, GraphQL, and SOAP APIs. Unlike an API scanner, it proves exploitability with evidence, tests authorization logic object by object, chains API weaknesses into multi-stage attack paths, and runs continuously as your APIs change.
FireCompass has been named a Sample Vendor for the Adversarial Exposure Validation use case in the Gartner® Hype Cycle™ for Security Operations, 2026, our fifth consecutive edition in this Hype Cycle.
Gartner, “Hype Cycle for Security Operations, 2026,” Darren Livingstone, Jonathan Nunez, 5 June 2026, ID G00846365.
Gartner does not endorse any vendor, product or service depicted in its research publications and does not advise technology users to select only those vendors with the highest ratings or other designation. Gartner research publications consist of the opinions of Gartner’s research organization and should not be construed as statements of fact. Gartner disclaims all warranties, expressed or implied, with respect to this research, including any warranties of merchantability or fitness for a particular purpose.
GARTNER and HYPE CYCLE are trademarks of Gartner, Inc. and/or its affiliates and are used herein with permission. All rights reserved.
Trusted by Avid Technology
Maker of tools used across Hollywood, broadcast and music
“The platform helps identify potential attack paths and highlight those that are exploitable.”
“FireCompass AI Agents have been valuable in supporting our continuous security assessment program. The platform helps identify potential attack paths and highlight those that are exploitable. It significantly reduces the time required for attack-surface discovery, initial testing, and evidence collection compared with a manual penetration-testing approach. This gives our Application Security team more time to focus on fixing and retesting. The FireCompass team has also been collaborative and responsive throughout the process.”
Curious what attack paths exist in your APIs? Book a 20-minute walkthrough with our team
Annual API pentesting cannot keep up with how fast APIs change
APIs now carry most application traffic and change every sprint. Most pentesting programs still run on a calendar. The gap opens across scope, depth, and speed at once, and attackers exploit all three.
Most API endpoints are never tested
- Documented APIs get tested; shadow and zombie endpoints do not
- Endpoints hide in JS bundles, mobile apps, and old API versions
- Attackers enumerate everything that is reachable
API findings are noisy and isolated
- Scanner false positive rates reach 70% or higher
- Broken object level authorization needs real context to prove
- Business logic abuse across API calls is scanner-invisible
Once-a-year testing cannot keep up
- Many organizations still test once per year
- Attackers exploit new CVEs in about 3 days
- New endpoints and versions ship every sprint
One agentic platform. Four jobs, done continuously.
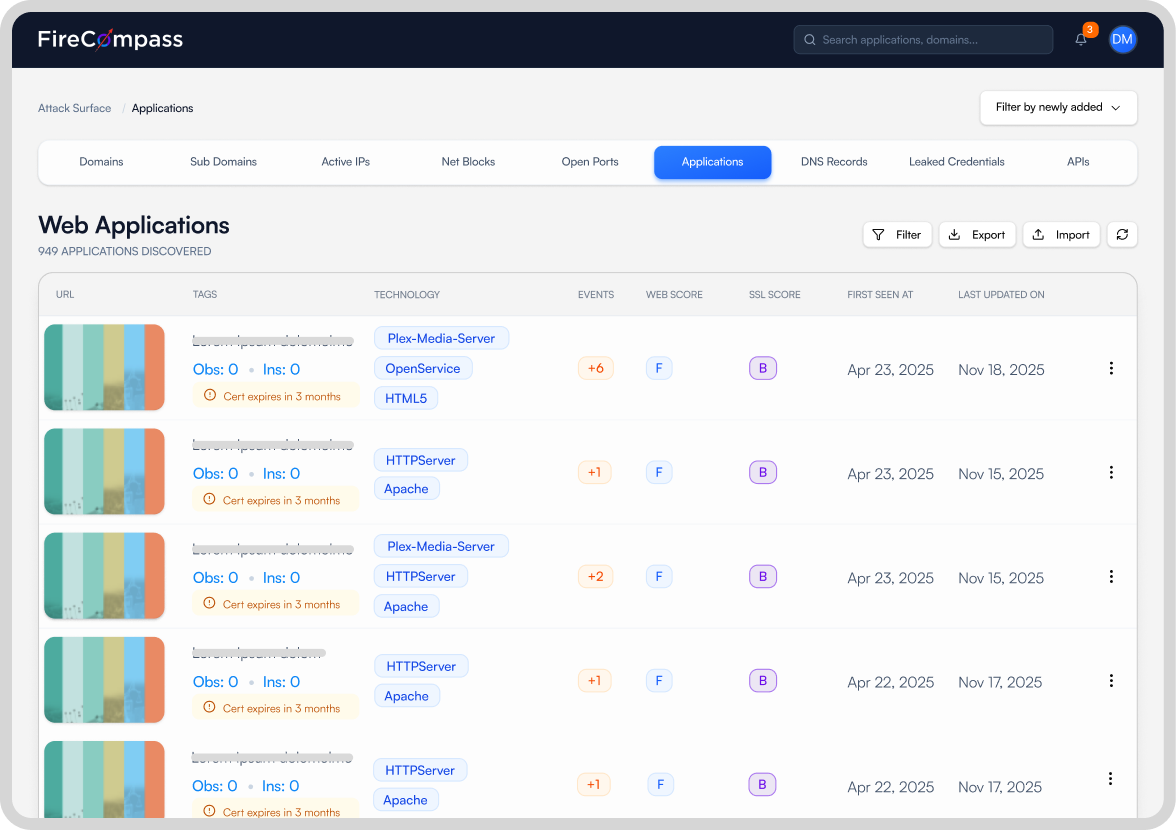
Find every API, including the shadow ones
The agent maps the APIs you do not have in your inventory, the endpoints attackers reach first.
- Endpoints pulled from JS files, mobile apps, and traffic
- OpenAPI, Swagger, and GraphQL schema discovery
- Deprecated and zombie API versions still reachable
- Leaked API keys and tokens on code repos and the dark web
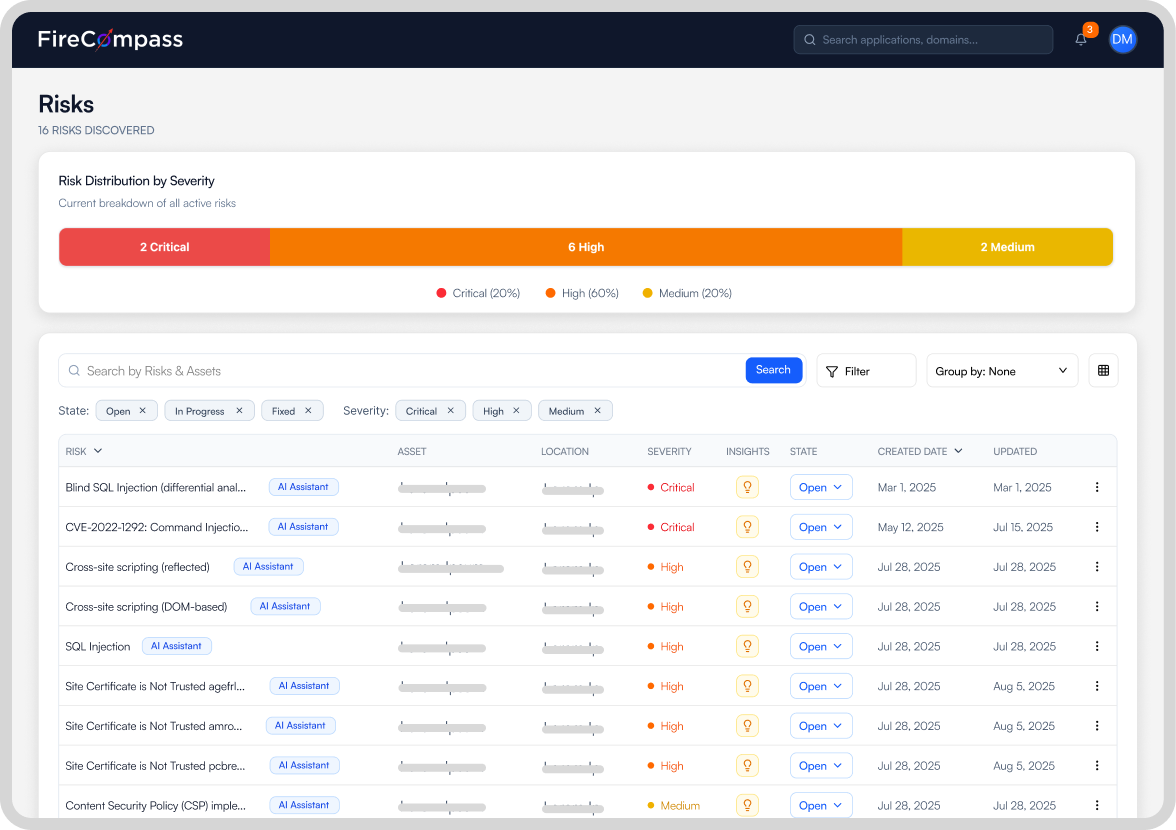
Prove what is exploitable
Every finding comes with a proof-of-exploit, not a maybe. That is how false positives stay under 2%.
- OWASP API Security Top 10 aligned coverage
- BOLA, IDOR, and broken function level authorization
- Authentication, token, and session weaknesses
- Mass assignment, injection, and rate-limit abuse
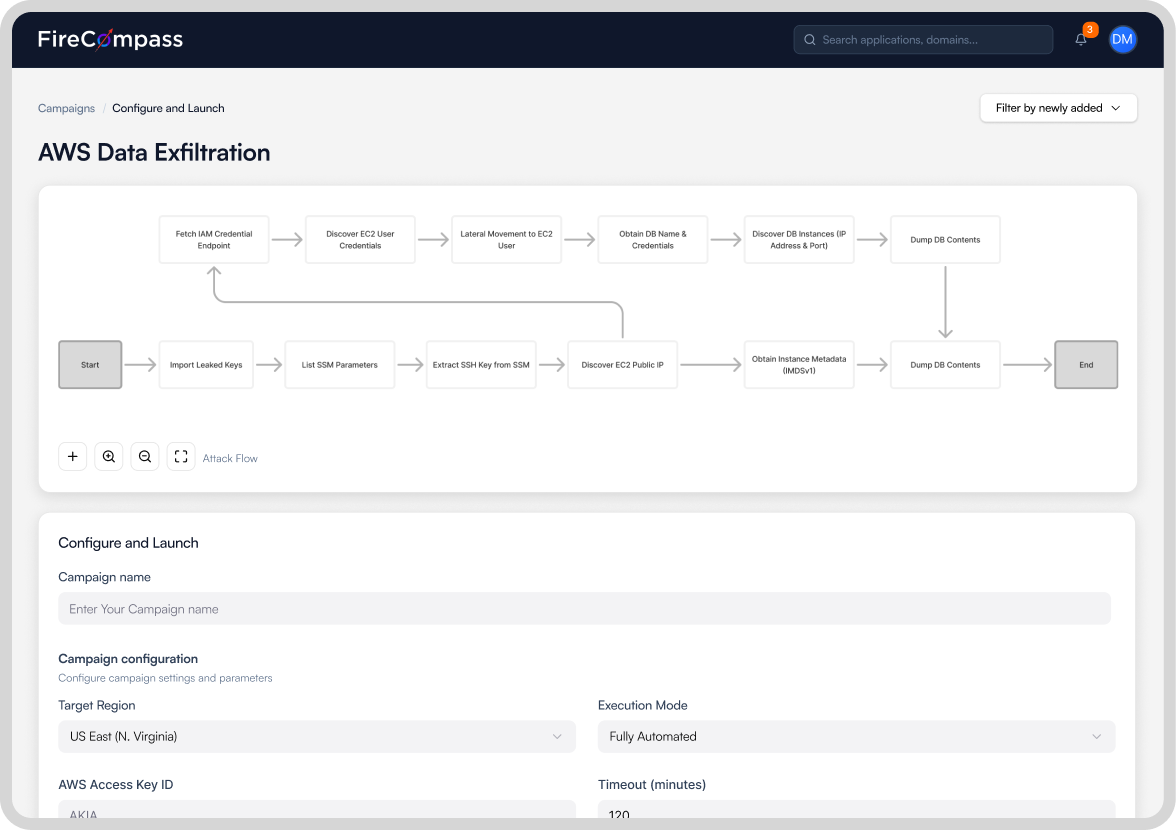
Show the true blast radius
An API flaw rarely stops at one endpoint. The agent links findings the way an attacker would, across APIs, apps, and into the network.
- Token and credential reuse across services
- API-to-app and API-to-infrastructure pivots
- Privilege escalation through chained API calls
- MITRE ATT&CK kill chain automation
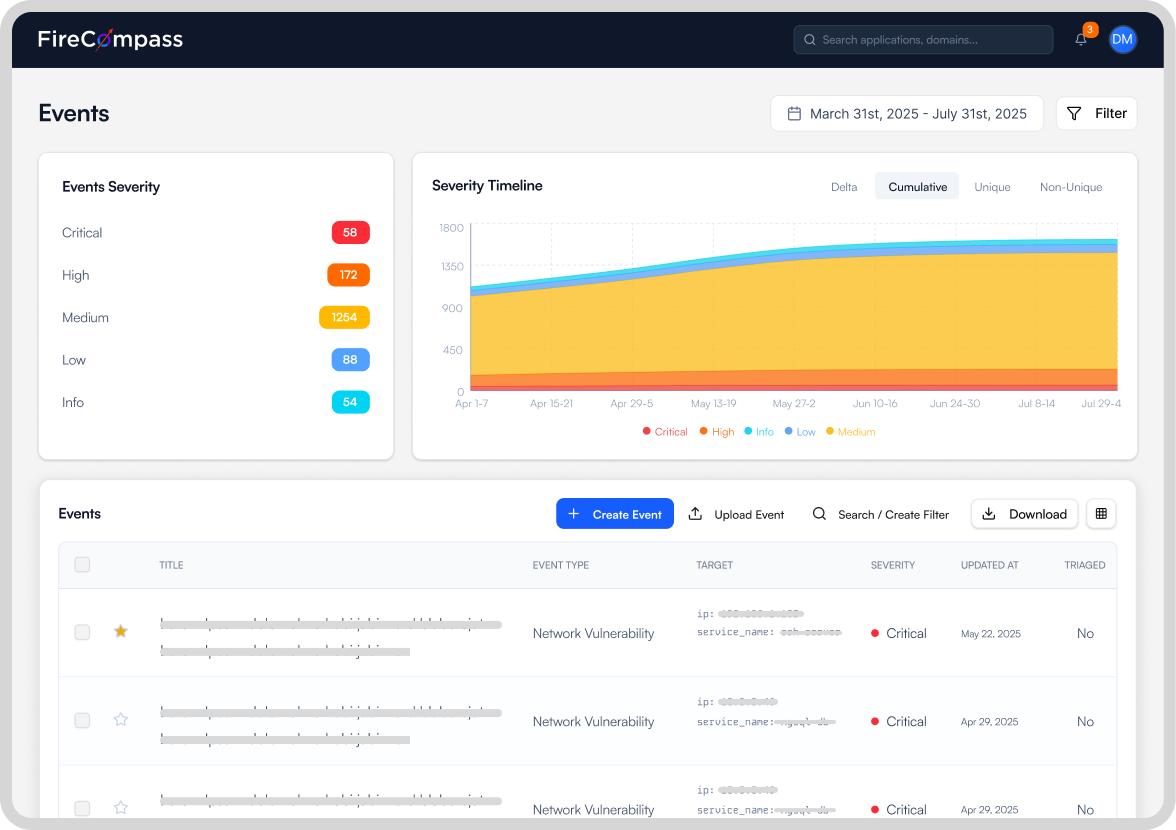
Run weekly, on-demand, or CI/CD-aligned
A new endpoint ships, a test fires. No scheduling, no waiting two weeks for a vendor slot.
- Day-1 validation for new CVEs
- One-click revalidation to confirm fixes
- Agentless, no install required
See it on your own APIs
Run a free AI pen test and watch the agent discover, exploit, and chain in minutes.
From a token in a JavaScript file to production access
No human steering. No predefined playbook. The AI agent turned a token left in a UAT JavaScript file into full production access, a path an API scanner would never connect.
Auth token in a .js file
The agent found an authentication token embedded in a JavaScript bundle on a UAT application.
Token decoded
It decoded the token and worked out which API calls and privileges it carried.
Restricted endpoints reached
The agent used the token against restricted API endpoints that were never meant to be reachable.
Production credentials
Those endpoints exposed production credentials, giving full production access from a UAT JavaScript file.
More real-world attack chains discovered by AI
Agentic AI platform for automated API pen testing and continuous red teaming
FireCompass AI closes the scope, depth, and speed gaps with a single AI-driven platform across APIs, web apps, and infrastructure.
Discover
- Shadow and zombie API endpoints
- Endpoints from JS files, apps, and docs
- Leaked keys and tokens
- Exposed API gateways and hosts
Pentest
- OWASP API Security Top 10 coverage
- Object and function level authorization
- Authentication and token attacks
- Proof-of-exploit for every finding
Chain & red team
- Token and credential reuse
- API-to-app and API-to-network pivots
- MITRE ATT&CK kill chain automation
- End-to-end red team scenarios
Continuously
- Weekly or on-demand pen testing
- Matches CI/CD release cadence
- Day-1 CVE validation
- Agentless, no install required
100% across every penetration testing benchmark
Fully autonomous, with no manual steering and no human hints, verified against industry-standard pentesting environments.
FireCompass AI vs. other API testing approaches
| Capability | FireCompass AI | Point-and-shoot AI | Leading DAST and API scanners | Manual PT |
|---|---|---|---|---|
| False positive rate | Under 2% | Variable | 40 to 70% | Low but variable |
| Shadow API discovery | Continuous | Limited | Documented specs only | Limited by scope |
| Authorization (BOLA) testing | AI-driven, multi-role | Limited | Pattern-based | Manual only |
| Attack chain discovery | Autonomous | Isolated findings | Single findings | Manual chaining |
| Red team scenarios | MITRE-aligned | Not supported | Not supported | Expert-dependent |
| Testing cadence | Weekly or per release | Per test | Scheduled scans | Once or twice a year |
$5,000 to under $1,000 per app. 2 weeks to 1 day.
Continuous AI-driven testing replaced a consulting firm's manual program across 2,000+ web applications.
Before: manual consulting
- About $5,000 per app per test, two consultant-days
- 2+ weeks lead time to schedule and complete
- 200 of 2,000+ apps tested annually
- Isolated findings, missed attack chains
- 70% false positive rate from DAST
After: FireCompass
- Under $1,000 per app, an 11x cost reduction
- On-demand testing, zero lead time
- Full coverage across 2,000+ apps continuously
- Chained attack paths consultants scoped out
- Under 2% false positive rate
Start with API pen testing. Expand to full red teaming and CTEM.
One platform covering PTaaS, automated red teaming, attack surface management, and continuous threat exposure management.
API & web automated pen testing
Authenticated and unauthenticated testing, authorization logic, and proof-of-exploit.
Infrastructure pen testing
Networks, servers, and cloud, continuously validated.
ExpandContinuous Automated Red Teaming
MITRE ATT&CK-aligned attack trees, lateral movement, and privilege escalation.
ExpandPTaaS, pen testing as a service
Expert-in-the-loop for business logic and compliance acceptance.
ExpandCTEM and attack surface management
Continuous exposure monitoring and risk prioritization.
SaaS or internal appliance
SaaS in minutes for external testing. Internal appliance in under one hour.
Trusted by Fortune 500. Recognized by Gartner, Forrester, and more.
30+ analyst reports
- Gartner 30+ reports, 5 technology maturity cycles, pen testing and CTEM
- Forrester Notable vendor, automated security testing
- IDC Innovator, cybersecurity
- GigaOm Radar Fast Mover, Platform Play (2024 to 2026)
- RSAC 365 Innovation Showcase
Fortune 500 customers
- Top 3 global telecom companies
- Top 10 IT companies
- Top 10 manufacturing firms
- Mid-sized banks and financial services
- Mid-sized automobile companies
Global presence
AI API penetration testing, answered
What is API penetration testing?
How is AI API penetration testing different from an API scanner?
Can FireCompass find shadow and undocumented APIs?
Does FireCompass test for the OWASP API Security Top 10?
Can FireCompass test authenticated APIs?
Is FireCompass recognized by Gartner for AI penetration testing?
GARTNER and HYPE CYCLE are trademarks of Gartner, Inc. and/or its affiliates and are used herein with permission. All rights reserved.
Is FireCompass ranked #1 on HackerOne?
HackerOne rankings are recalculated daily; positions are as captured on the dates stated. HackerOne is a trademark of HackerOne Inc. and has not endorsed these results.
Is there a free API penetration test?
Go deeper
Start your free API pen test today
Free attack surface scan. No agents to install. Results in minutes.