FireCompass vs Promptfoo
#1 on HackerOne* Start free test ↓Finding a bug is only half the job. Promptfoo tests your prompts. FireCompass AI pentests the whole app around them (web, APIs and AI agents), proves, fixes and retests, free.
Autonomous AI agents test your web apps and APIs like a real attacker, prove what is exploitable, and chain findings into full attack paths.
“The platform helps identify potential attack paths and highlight those that are exploitable. It significantly reduces the time required for attack-surface discovery, initial testing, and evidence collection.”
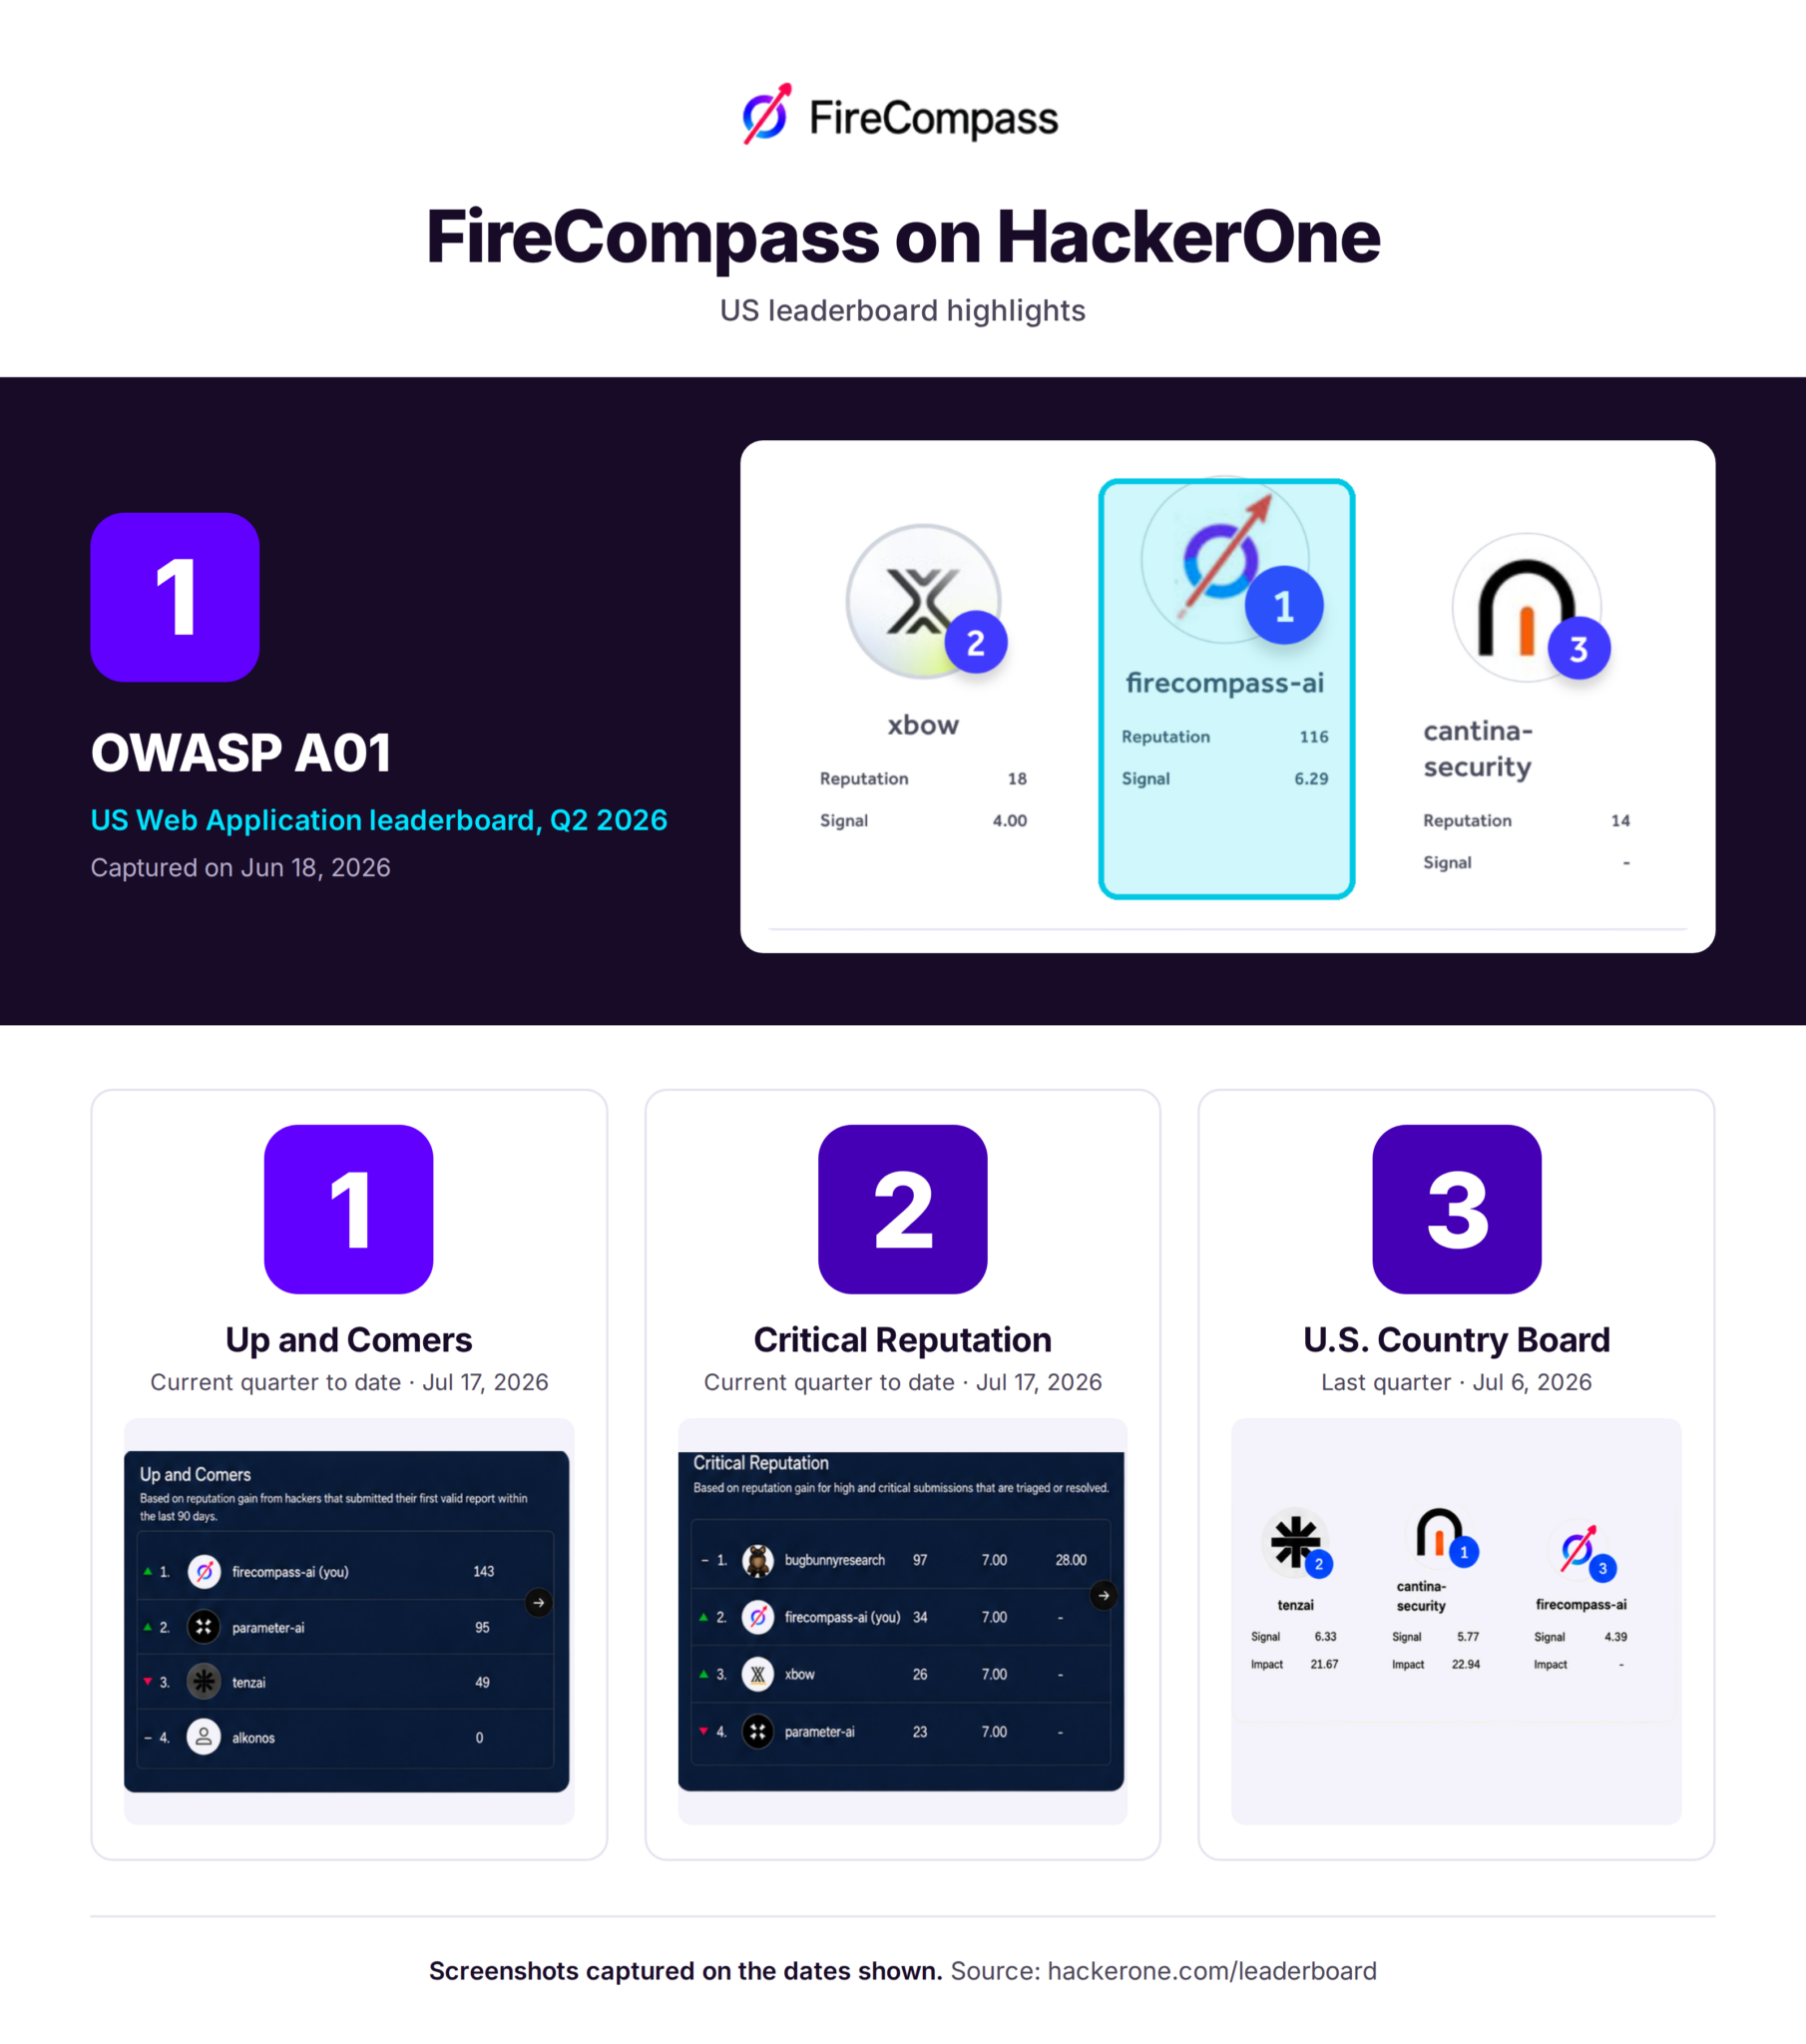
FireCompass on HackerOne
* #1, #2, #3 in multiple HackerOne leaderboards during Q2 & Q3 2026. Source: hackerone.com/leaderboard
Compare them on your own app, free
Put the #1 AI hacker to the test. See the attack paths it can chain.
How it works in 60 seconds
- Submit the form. Use your work email and the app you want tested.
- A short kickoff call, then access. We agree on scope, understand your success criteria, and initiate AI agent access.
- AI agents run. Nothing to install. Proven findings, each with exploit proof and a fix, in about a day.
FireCompass vs Promptfoo across key areas.
Promptfoo tests the model. FireCompass tests the app wrapped around it, and proves the fix.
| Capability | FireCompass | Promptfoo |
|---|---|---|
| What gets tested | The whole app around your AI.Web app, APIs, authentication and the infrastructure your AI features run on. | |
| Business logic and access control | Logic-aware, authenticated testing.Business logic, IDOR, BOLA and broken access control, alongside OWASP Top 10: 2025. | |
| Attack-path chaining | Multi-stage attack paths.Chains findings from the app into APIs and infrastructure, end to end. | |
| Proof | Proof of exploit on every finding.Under 2% false positives, with steps to reproduce and a fix. | Shows the failing prompts and model responses. |
| Who runs it | Autonomous AI agents.Nothing to configure or script. Re-run after a fix to confirm it held. | Developers write and run test configs, often in CI. |
| Public results | #1, #2, #3 in multiple HackerOne leaderboards*and 100% on XBEN, Acuart and DVWA. | Check their latest published results. |
| Where they are strong | Proven findings across the whole app, chained into attack paths, with a closed loop to the fix. | Genuinely strong here: open-source, developer-friendly LLM evals and red teaming. |
* #1, #2, #3 in multiple HackerOne leaderboards during Q2 & Q3 2026.
Promptfoo details are based on Promptfoo’s public materials and third-party comparisons as of October 2026. If anything here is out of date, tell us and we will correct it.
FireCompass vs Promptfoo: common questions
What is the difference between FireCompass and Promptfoo?
Promptfoo tests LLM models and prompts for jailbreaks, prompt injection and unsafe output. FireCompass AI pentests the whole application around your AI: web app, APIs, authentication, business logic and infrastructure, with multi-stage attack paths and a working exploit on every finding.
How does FireCompass rank on HackerOne?
FireCompass AI is the #1 AI on HackerOne. It ranked #1, #2 and #3 across multiple HackerOne leaderboards during Q2 and Q3 2026.
Can I compare FireCompass and Promptfoo on my own app?
Yes. The free AI pen test runs on your own web apps and APIs with 4,000 credits and no credit card. Every finding comes with a working exploit, evidence and steps to reproduce, so you can compare results side by side.
Trusted by Avid Technology
Maker of tools used across Hollywood, broadcast and music
“The platform helps identify potential attack paths and highlight those that are exploitable.”
“FireCompass AI Agents have been valuable in supporting our continuous security assessment program. The platform helps identify potential attack paths and highlight those that are exploitable. It significantly reduces the time required for attack-surface discovery, initial testing, and evidence collection compared with a manual penetration-testing approach. This gives our Application Security team more time to focus on fixing and retesting. The FireCompass team has also been collaborative and responsive throughout the process.”
Curious what attack paths exist in your apps? Book a 20-minute walkthrough with our team
Exploit-validated findings, benchmarked in the open.
$5,000 to under $1,000 per app. 2 weeks to 1 day.
Before: manual consulting
- About $5,000 per app, two consultant-days
- 2+ weeks lead time per engagement
- 200 of 2,000+ apps covered, roughly 10 percent
- Isolated findings, no attack chains
After: FireCompass agents
- Under $1,000 per app, about 11x lower
- 1 day lead time, continuous cadence
- 2,000+ apps, about 99 percent of the surface
- Chained attack paths, under 2 percent false positives
What you get from your free AI pen test.
- OWASP Top 10: 2025 plus business logic, authenticated and unauthenticated paths.
- A full pen test report you can share with your team, your auditors, and your customers.
- Access to the FireCompass portal to explore every finding and attack path in one place.
- A working proof-of-concept exploit validated live by an AI agent, not a theoretical flag.
- Evidence, steps to reproduce, and ready-to-run Python for every finding.
Case Study of Agentic Attack Chaining: Combining Low and Medium Vulnerabilities To Exploit A Database
No human steering. No predefined playbook.
- Exposed .git. The agent reconstructed the repo and pulled database credentials from config files.
- Direct DB access blocked. The port was not externally exposed. A scanner stops here.
- Credential reuse to SSH root. The agent tested the same creds against SSH and gained root.
- Internal pivot to data exfiltration. It found private keys, pivoted, and dumped the database.
Autonomous only works if it is safe to run in production.
An attacker inside your environment, even your own, needs rules. We built the controls before we built the demo, because the reliability concerns raised about unsupervised adversarial testing are correct.
- Scope enforcementAgents act only on authorized assets; out-of-scope hosts are discovered, never touched.
- Production-safe exploitationImpact is demonstrated, not caused. Rate limits and safe payloads by default.
- Forensic audit trailEvery request and decision logged and replayable for your auditor.
- Human approval gatesHigh-impact actions wait for a human, if you want them to.
- Kill switchesStop any run, any agent, instantly.
The #1 AI hacker, recognized by analysts and trusted by the Fortune 500.
Compare FireCompass and Promptfoo on your own app, free
Watch an AI agent discover, exploit, and chain across your own web apps and APIs, with a working exploit on every finding.
Start Your Free Pen Test →- 4000 credits, no credit card
- Proof of exploit on every finding
- Production-safe, scope-enforced agents