#1 on HackerOne*See a demo of how AI pen test agents work
30 minutes on a screen share. What the AI pen test agents do on web apps and APIs, and what your team gets at the end. Agenda below.
- 30 minutes on a screen share, with the agenda below
- A FireCompass security expert on the call
- Nothing to install. No agents, no deployment window
* Ranked #1, #2 and #3 across multiple HackerOne leaderboards during Q2 and Q3 2026.
Book a demo
Tell us where to reach you. We call first to confirm scope and fit, then book the demo.
Authorized testing only. Nothing is tested without written scope approval. See our Privacy Policy.
What we show you in 30 minutes
Multi-stage attacks
How the agents chain findings into a full attack path, the way a human red teamer would. An exposed file leads to credentials, credentials lead to root, root leads to the database.
Business logic flaws and IDOR
The classes scanners and most pen testing tools miss. The agents find them and prove they are exploitable.
The reporting engine
Proof of exploit, steps to reproduce, and severity scored against reachability, so your team gets a fix order rather than a list.
Cost and speed
Where the 80% cost saving and 20x velocity come from, against what you spend on pen testing today.
“It significantly reduces the time required for attack-surface discovery, initial testing, and evidence collection compared with a fully manual penetration-testing approach. This gives our Application Security team more time to focus on validating findings, coordinating with system owners, prioritizing remediation, and planning retesting.”
Exploit-validated findings, benchmarked in the open.
The leaderboard, unedited.
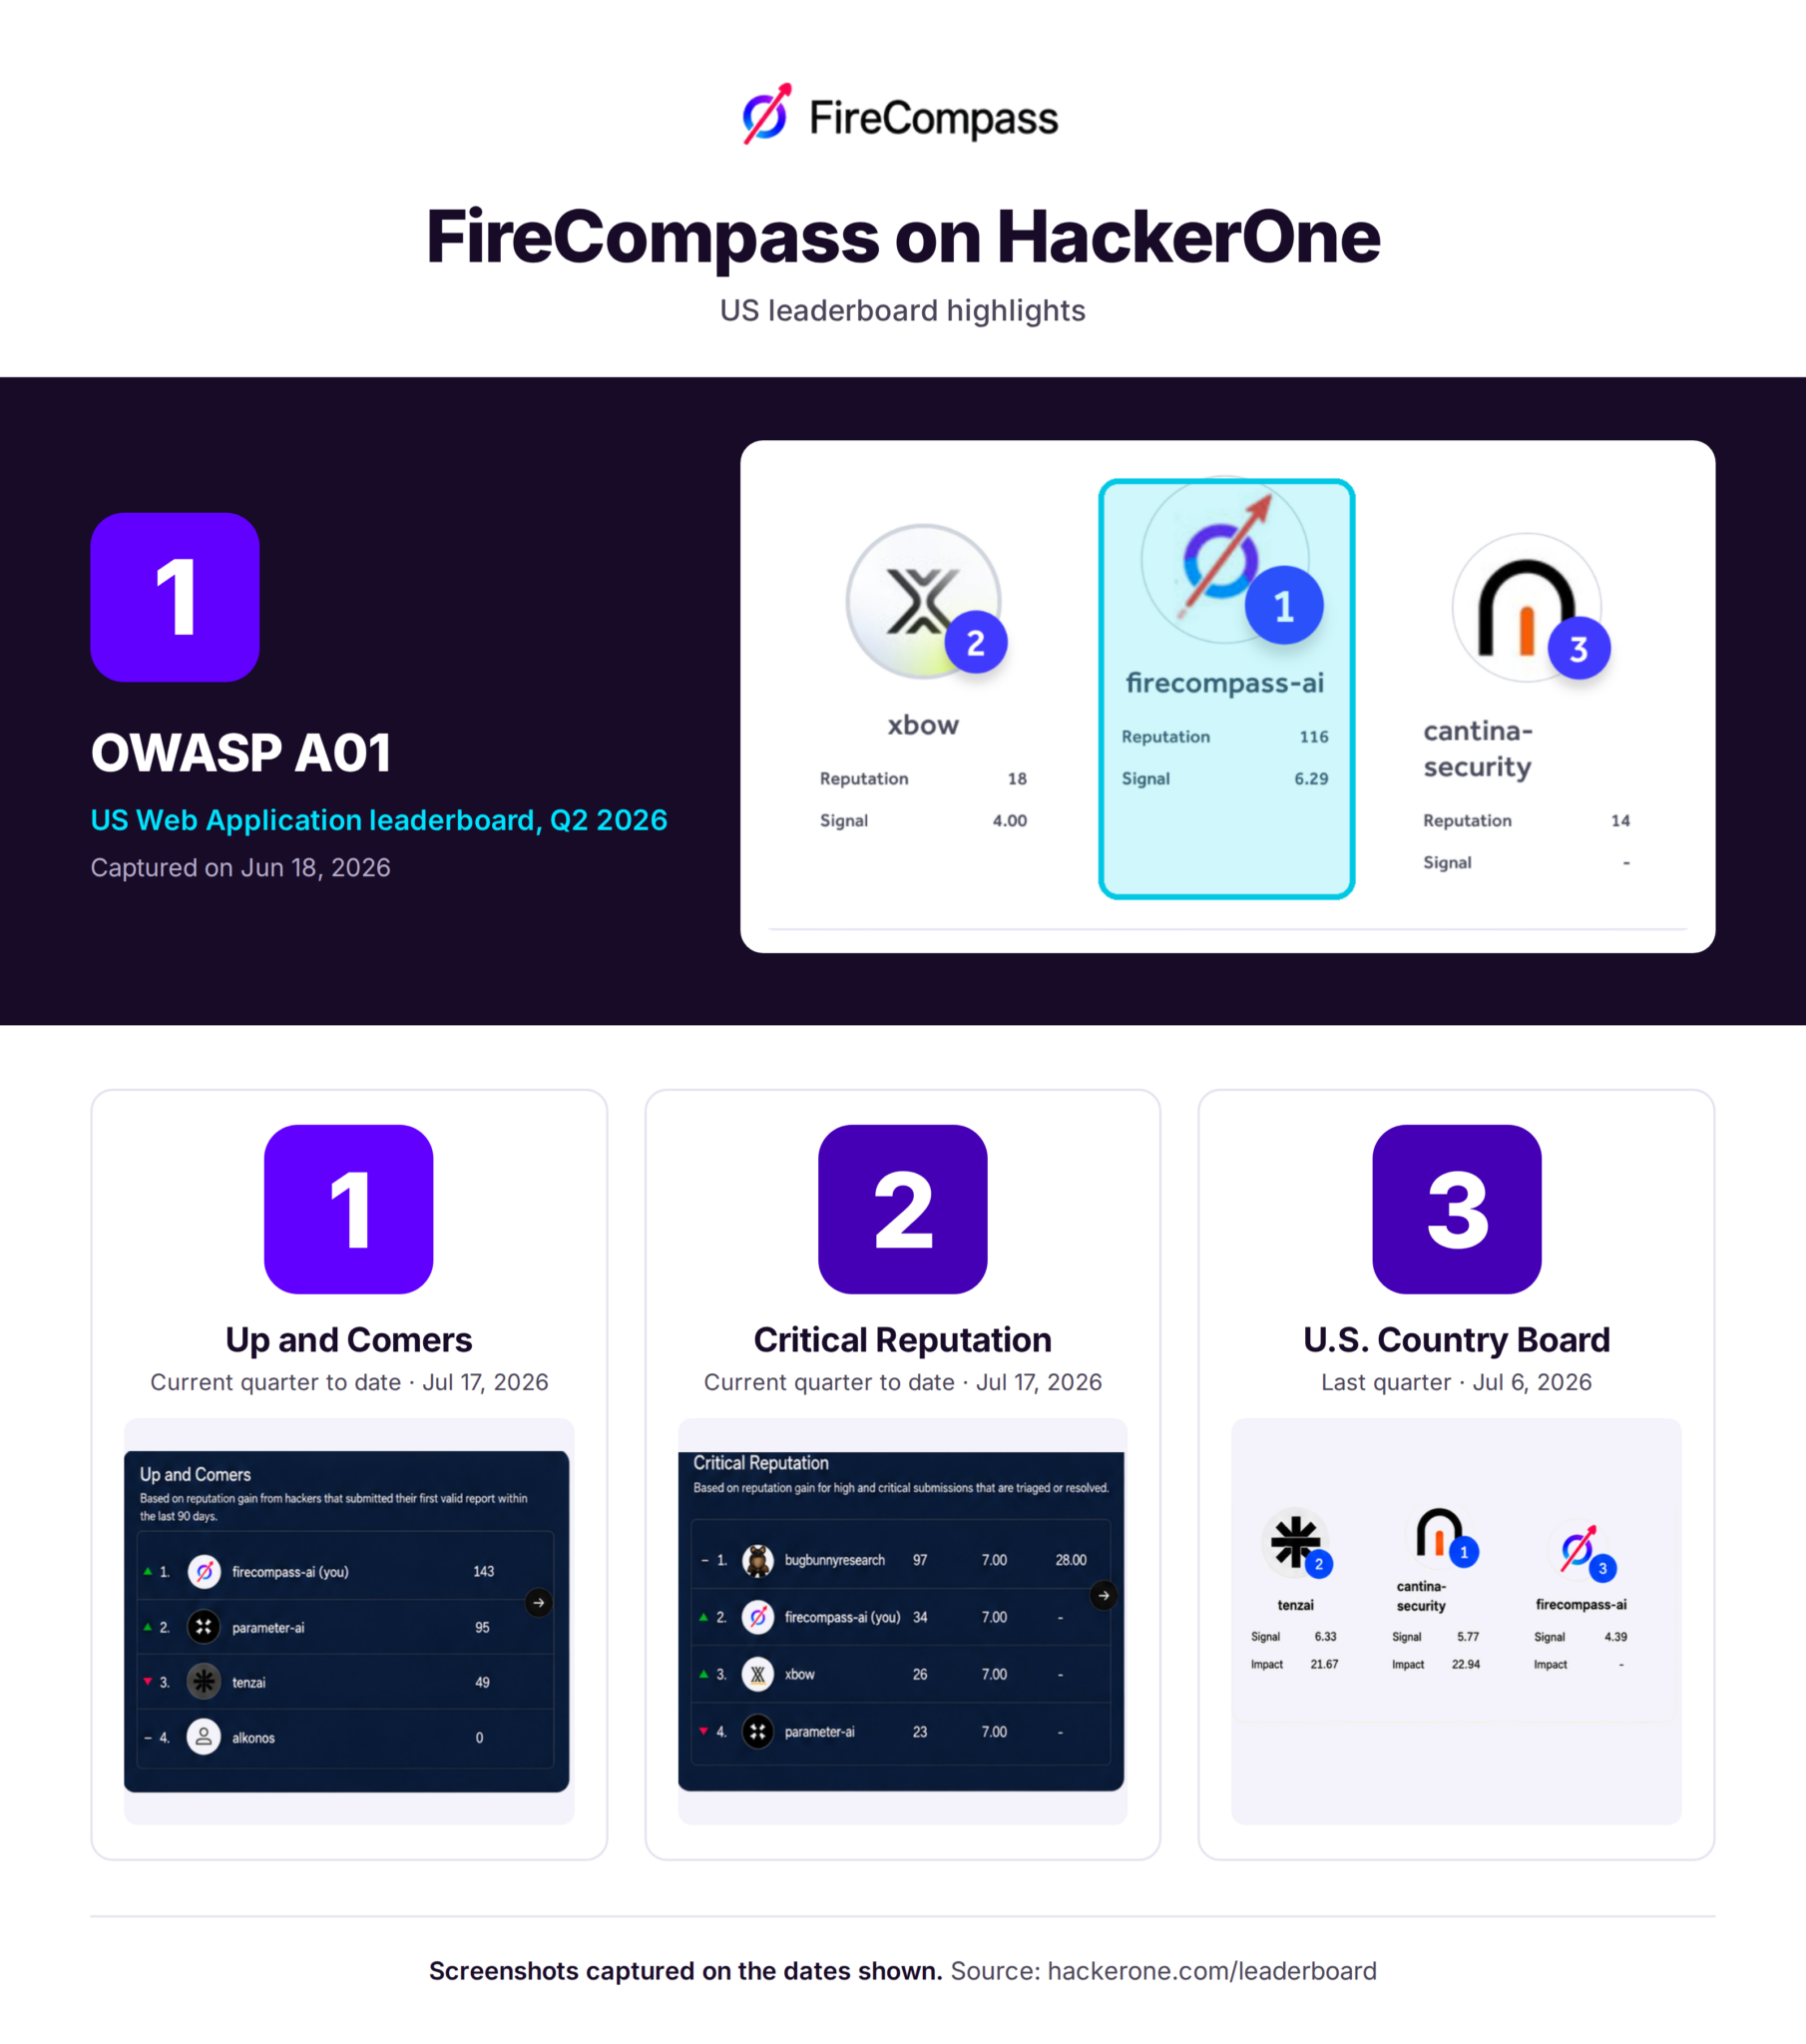
The #1 AI hacker, recognized by analysts and trusted by the Fortune 500.
Put the #1 AI hacker on your attack surface.
Watch an AI agent discover, exploit, and chain across your apps and APIs in minutes.
Book a Demo →